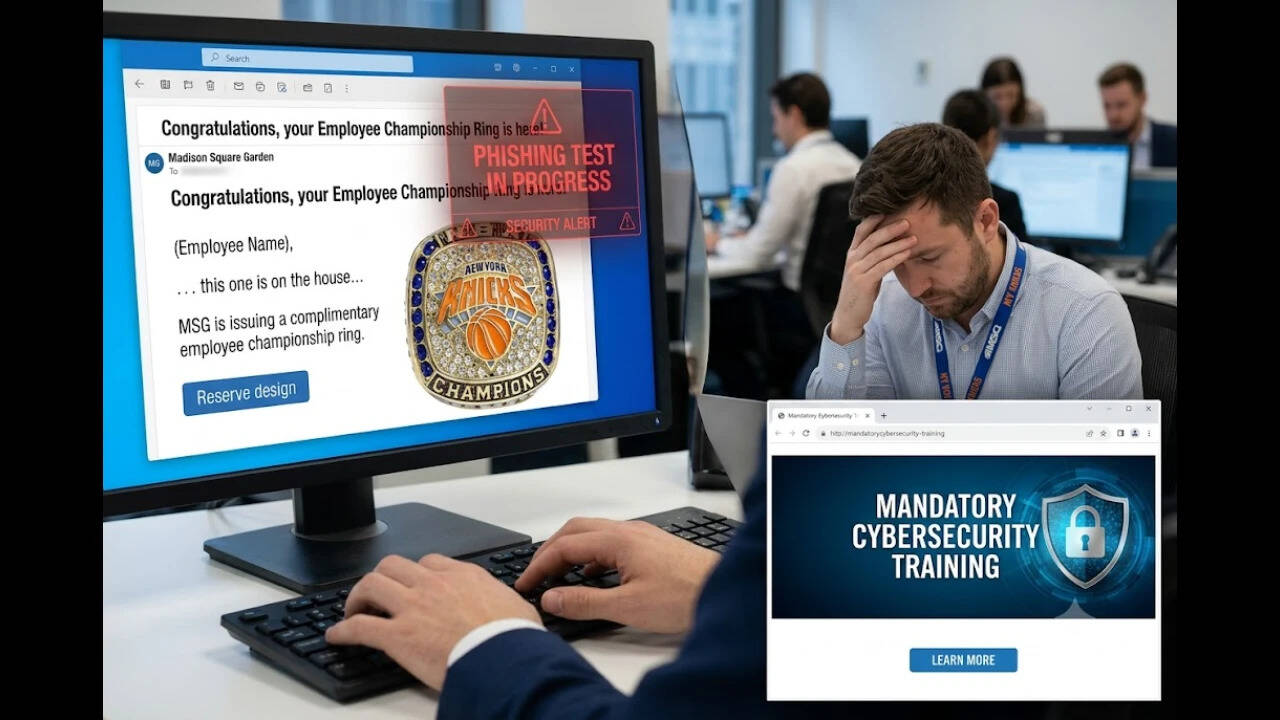
Madison Square Garden Sports, the parent company of the New York Knicks, has admitted that an email offering staff free NBA championship rings was a phishing test. Employees who clicked to reserve a ring were sent to a mandatory cybersecurity class instead.The company has now called it an "unfortunate mistake." It says it will hand out more than 275 championship rings and pieces of jewellery, worth over $3.7 million, to players, coaches, employees and others in the organisation. The timing made the episode sting. The Knicks won the 2026 NBA title in June, their first since 1973, and the franchise is still in the middle of celebrating it. The Knicks championship ring email was built to look official The email went out to a long list of MSG employees in late September, weeks before the team's ring-and-banner ceremony. According to The Athletic, which obtained a copy, it opened with a graphic of two ring styles and the line "Congratulations, your Employee Championship Ring is here."Each employee was addressed by name and told the ring was complimentary, personalised and made by the same jeweller as the players' rings. There were two designs to pick from: Championship Gold and Garden Classic.It was an easy offer to believe. Most NBA team employees receive a ring after a title, even if it is a simpler version of what the players wear. Team sources told The Athletic that those who clicked were put through a cybersecurity class tied to owner James Dolan's growing concerns about hacking. MSG says a real phishing attack led to the test MSG's first response to The Athletic was short: "We are not disclosing anything about the rings." A day later, the company changed course. A spokesperson said the email was a phishing simulation sent to the corporate team to strengthen its security against hackers."MSG was recently hacked and extorted using an employee login and password obtained through a similar phishing attack," the statement said. It added that using the rings as a lure "was an unfortunate mistake."Phishing drills are routine at large companies, so the criticism is mostly about the bait. Guidance from the US National Institute of Standards and Technology says such exercises should not be punitive. GoDaddy faced a similar backlash in 2020, when a fake holiday bonus email to staff turned out to be a security test. Prize-themed phishing tests draw clicks, but security agencies warn against punishing staff From a pure security standpoint, the ring was an effective lure. Attackers often dress up phishing emails as rewards because people act on them quickly and without much thought. In a recent report, Kaspersky found that a FIFA-themed phishing simulation offering prizes for wearing a national team jersey got a 66% click rate.The trouble lies in what happens after the click. The UK's National Cyber Security Centre says punishing employees for falling for a test email can start to look like entrapment. It also advises companies to check with HR before sending anything that could upset staff, which a fake championship ring offer was always likely to do.Security tech has been a sore point at MSG for a while. The Garden has used facial recognition at its entrances since at least 2018, and in 2023 it was reported to have used the system to turn away lawyers from firms involved in litigation against the company. A database leaked earlier this year also showed MSG assigning risk scores to celebrities and their guests.MSG has not said how many employees clicked the September email, or whether it plans to change how it runs these tests.
New York Knicks emailed staff free championship rings, those who clicked got a surprise
Madison Square Garden Sports has admitted that an email offering New York Knicks employees free NBA championship rings was a phishing test. Staff who clicked were sent to a mandatory cybersecurity class, The Athletic reported. MSG called the ring lure an "unfortunate mistake," citing a recent hack that used stolen employee credentials, and says it will now gift more than 275 rings and jewellery worth over $3.7 million.
Read the full story at Times of India.